Cybersecurity · 4 min read
Patching: the security control most organisations aren’t measuring
Firewalls get the budget, but unpatched devices remain one of the most common ways attackers get in. Here is how to make patching measurable.
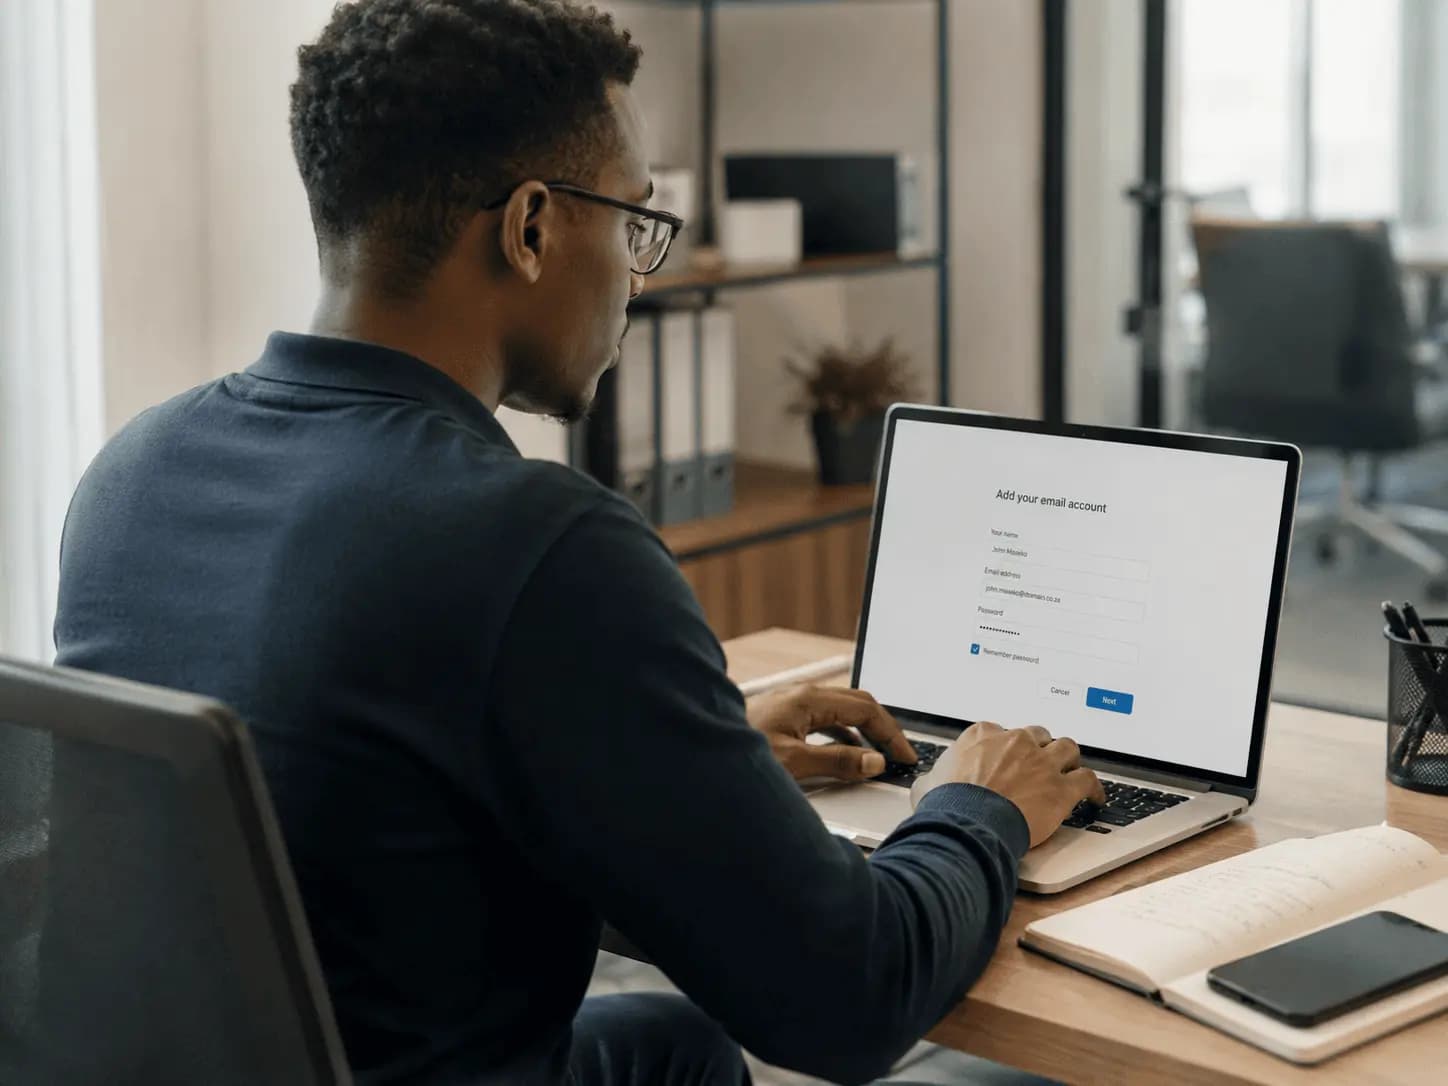
When organisations think about cybersecurity, they usually think about firewalls and antivirus. Both matter. But one of the most reliable ways attackers gain access is still an unpatched device or application with a known vulnerability.
Why patching slips
Patching competes with everything else IT has to do. Updates are postponed to avoid disruption, remote devices are rarely connected, and nobody has a single view of which machines are behind. The result is a risk that grows quietly.
Make it visible
Centralised patch management changes the question from “did we patch?” to “what percentage of our estate is current, and which devices are not?” That number belongs in your monthly IT report.
If you can’t report your patch compliance, you can’t manage it.
Make it routine
Agree maintenance windows, test updates on a pilot group, then deploy in waves. Combine patching with network monitoring so you can see the impact of changes in real time.
Make it accountable
Whether patching is done in-house or by a partner, define who owns it, what the target is and how exceptions are handled. Good governance turns a technical task into a managed control.
Published by Digital Express Technologies.
Talk to our Cybersecurity Protection team.
SOC/SIEM, 24/7 monitoring, testing and compliance reporting.
More insights
Where AI voice agents actually help — and where a person still matters
AI agents are not a magic receptionist. Used in the right places, they stop enquiries going unanswered and free your team for work that needs judgement.
What a good IT support agreement should actually include
A monthly fee is not a service level. Seven things to check before you sign a managed IT agreement.
Five questions to ask before your next network upgrade
Most network problems are designed in long before the first cable is pulled. These five questions separate a lasting upgrade from an expensive patch.